Managed SOC
Round-the-clock monitoring, detection and response, built for government, telecom and enterprise networks that need data to stay in their control.
What you get
Collection and parsing
Syslog, SNMPv3, NetFlow, Windows Event Forwarding and APIs, with custom parsers for carrier and network equipment.
Detection
Correlation mapped to MITRE ATT&CK, UEBA baselines and threat intelligence matching.
Response
Playbook-driven containment with human approval, rollback and a full audit trail.
Reporting
Executive dashboards, SLA and MTTR reporting, with drill-down to the underlying events.
Local-first AI
Analyst summaries from models running on your infrastructure, with evidence shown for each claim.
Resilience
High availability and disaster recovery with recovery times that are tested, not asserted.
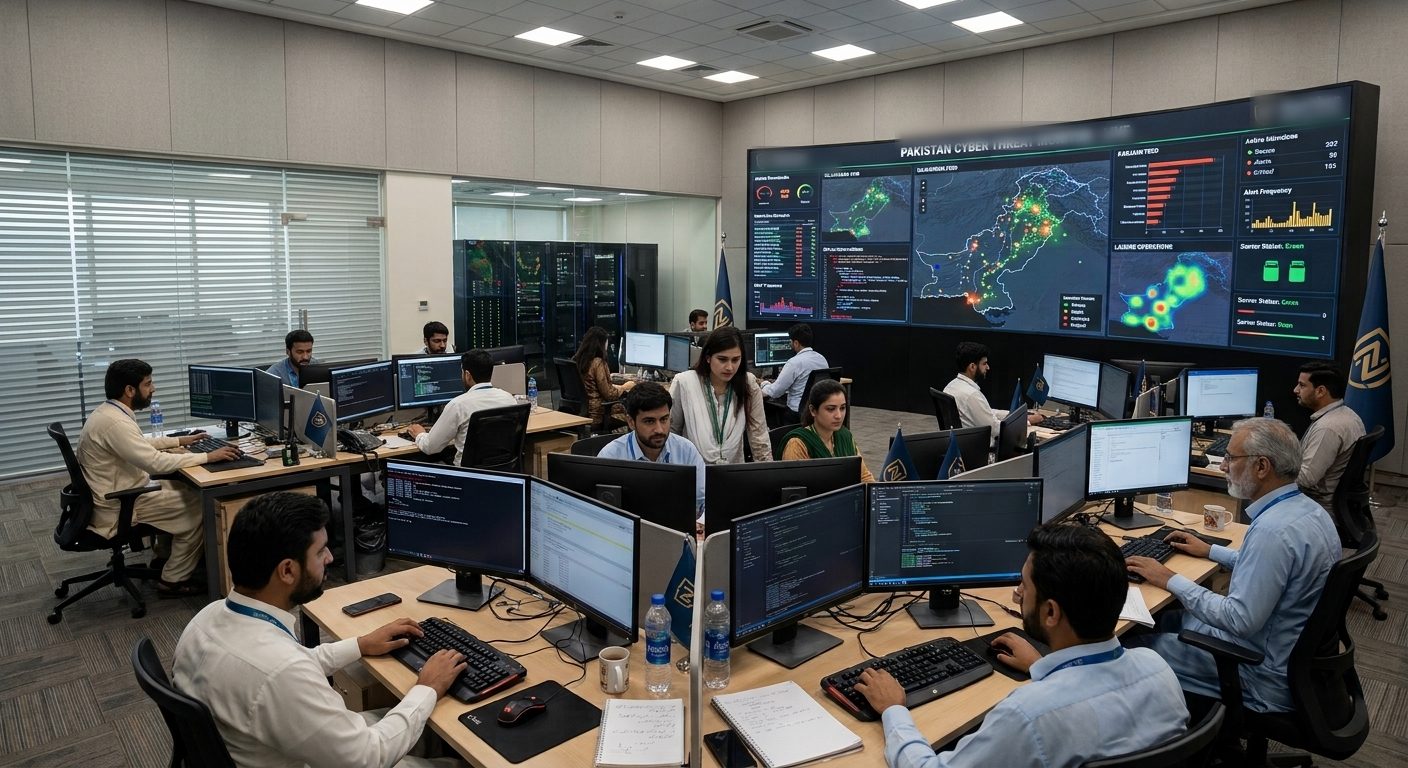
How it works, illustrated
Standards we map to
How it runs
- Discover. Inventory log sources, assets and existing tools.
- Design. Size capacity, parsers, HA and DR.
- Onboard. Integrate sources, tune detections and train your team.
- Operate. Monitor, respond and report continuously.
Questions
Can your SOC run without internet access?
Yes. We design for local-only operation, where external lookups can be switched off without losing core detection, search and reporting.
Who owns the data?
You do. Telemetry stays in your environment and every outbound connection is documented and controllable.
Do you replace our existing SIEM?
Not necessarily. We can integrate with or migrate from tools such as Wazuh or Graylog, depending on your goals.